Know what's exposed in Microsoft 365 before you scale Copilot and AI.
Identify overshared sensitive information, excessive permissions and unmanaged content before expanding Copilot and AI across your organisation.
IMGC EXPLAINED
Information Management, Governance and Compliance
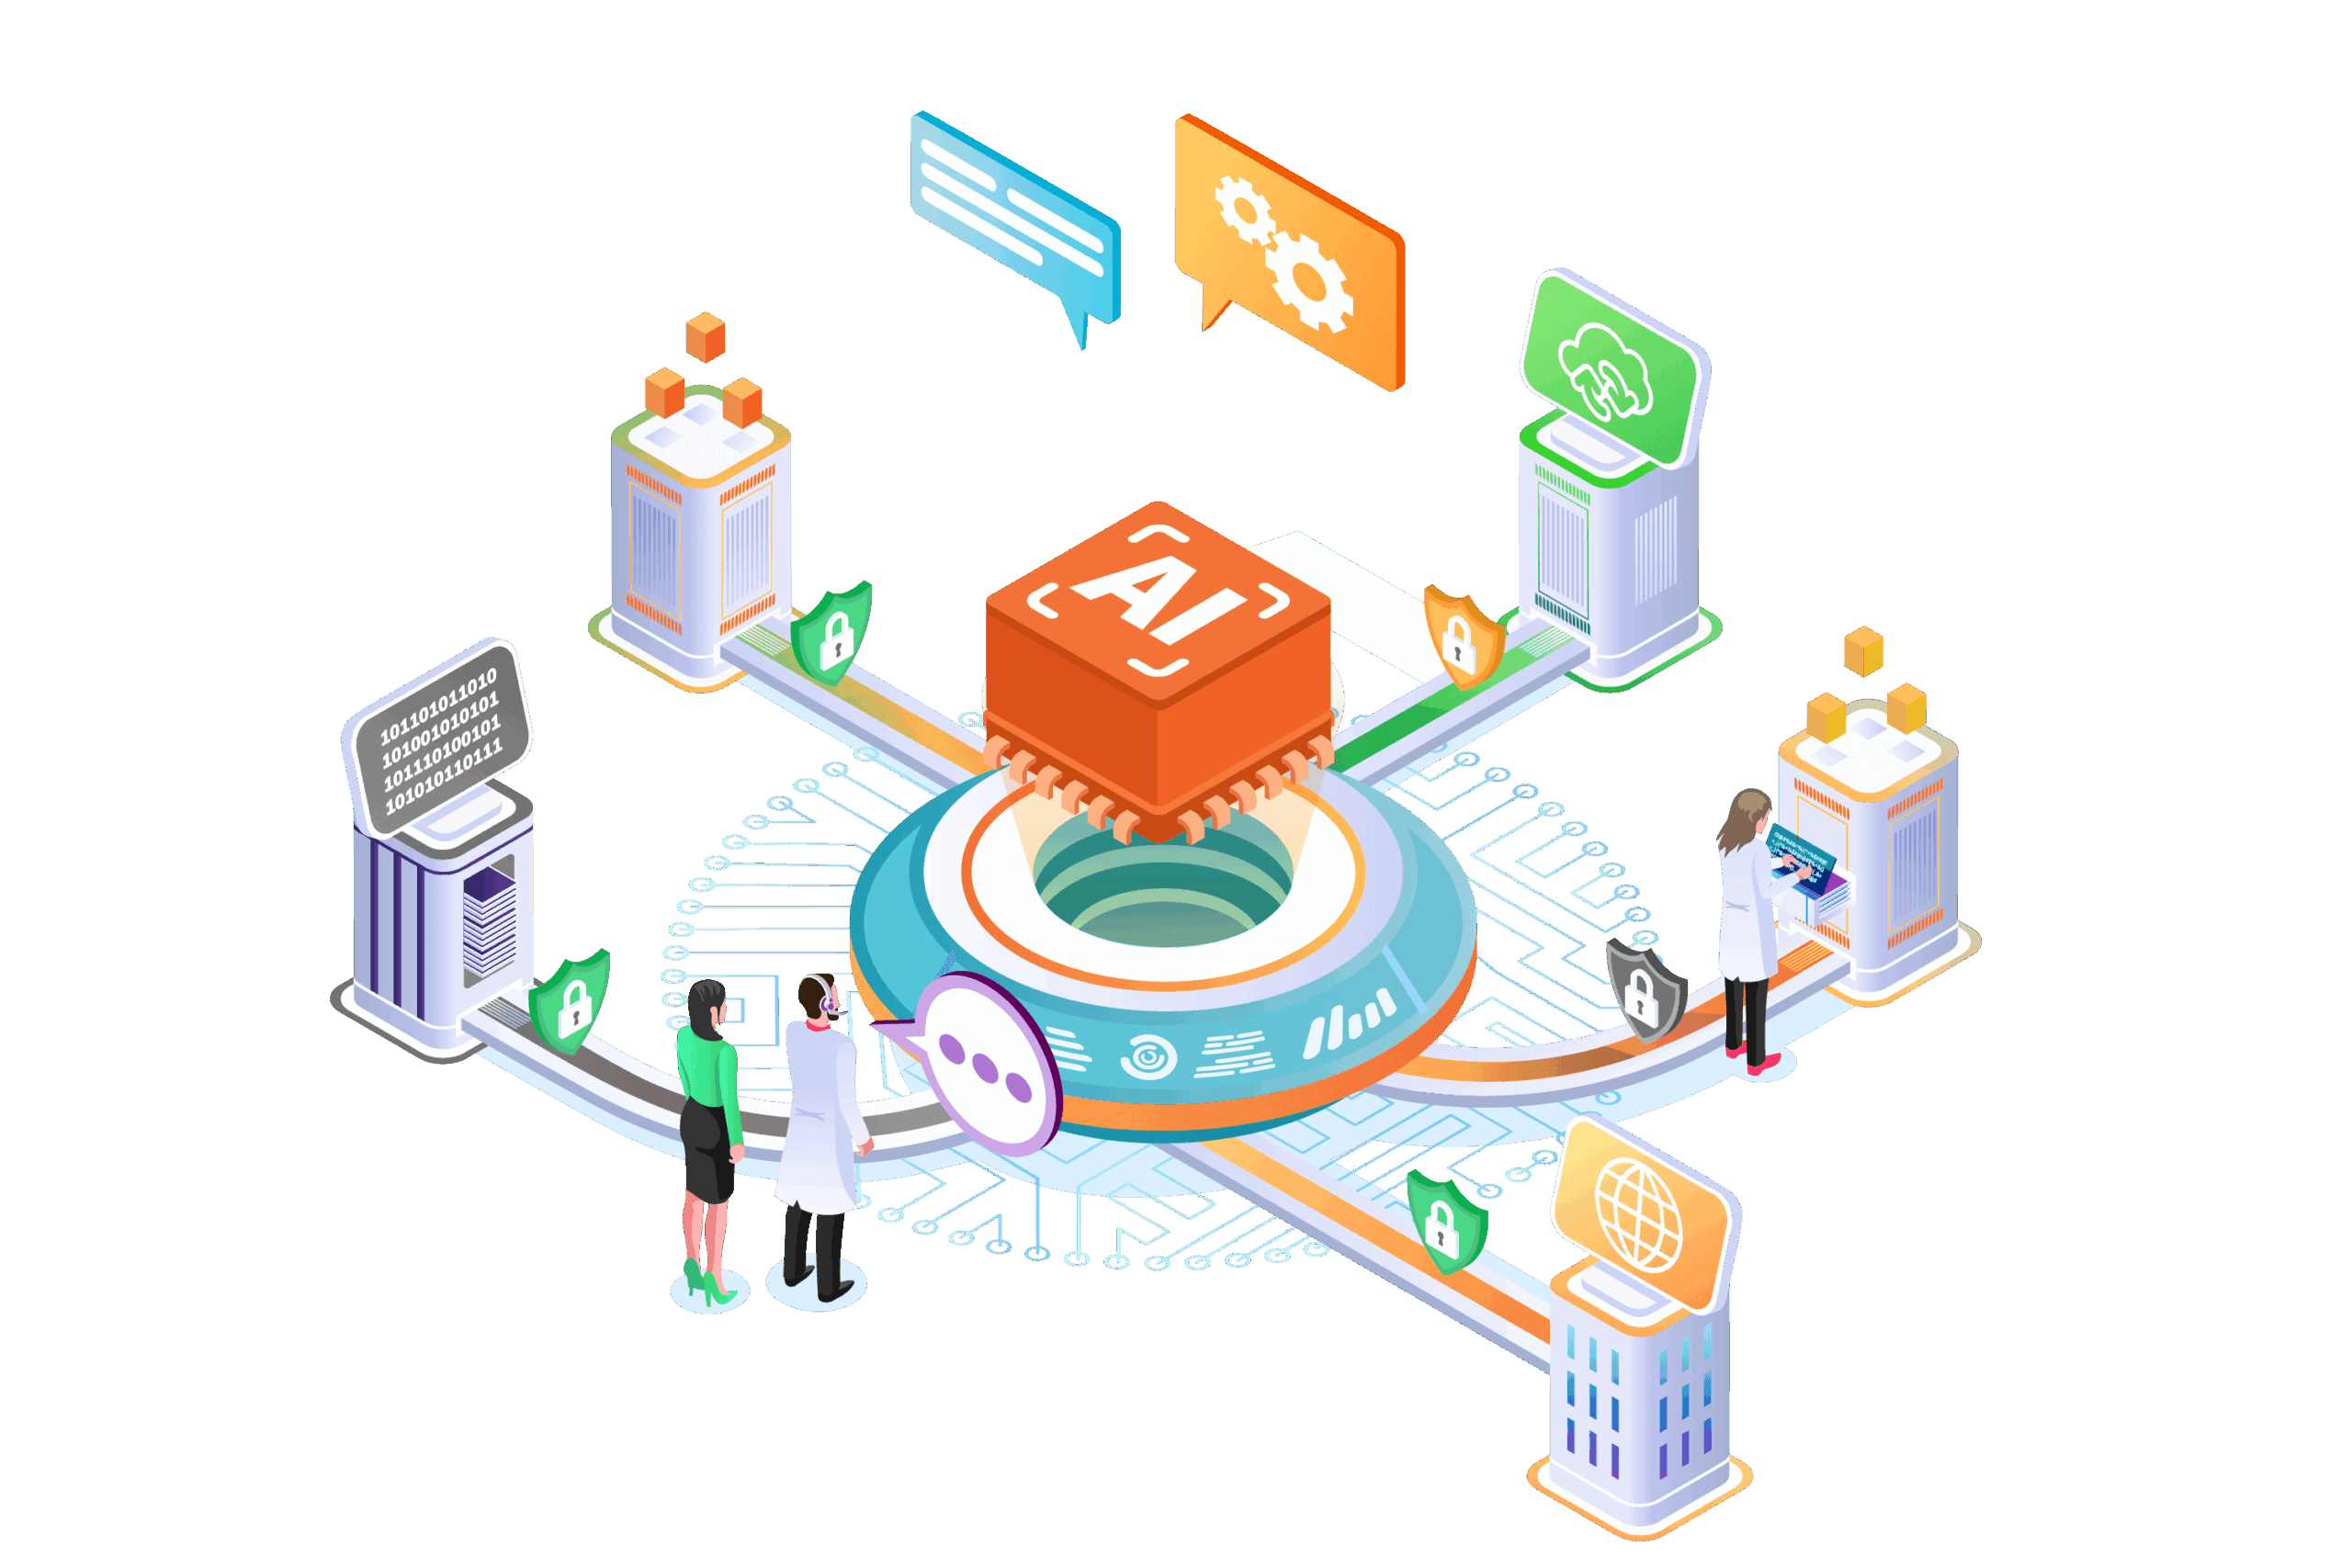
IMGC helps organisations understand, protect and govern information across Microsoft 365.
Insentra combines governance expertise with Microsoft technologies to reduce information risk, strengthen compliance and ensure your data is ready for Copilot, AI agents and automation.
Proven IMGC expertise. Built on Microsoft experience at scale.
4M+
Microsoft 365 Seats Governed
5,500+
Projects Delivered Worldwide
95
NPS Score
Microsoft Advanced Specialisation
Modern Work, Identity & Security
THE CHALLENGE
Your Microsoft 365 environment has grown faster than your ability to govern it.
Years of uncontrolled growth have left sensitive information overshared, permissions unchecked and content scattered across Microsoft 365. Until now, much of that risk stayed hidden. Copilot and AI agents change that. They can find, surface and act on information at a scale people never could, turning years of information debt into security, compliance and business risk almost overnight.
COMMON BUSINESS PROBLEMS WE SOLVE
If any of this sounds familiar, you are not alone.

Copilot is exposing existing risk
Overshared, poorly classified and unmanaged information can become easier for users and AI to find and act on.

You don’t know who can access what

Governance hasn’t kept pace

Compliance is getting harder to prove
How many of these risks are hiding in your Microsoft 365 environment?
HOW WE DELIVER IT
A staged journey. Crawl, Walk, Run.
Each stage delivers value before you commit to the next.
See and Understand Your Risk.
What you get
A classified, governed baseline with risks visible and nothing disrupted for your users.
What we do
- Discover and classify sensitive information
- Assess permissions and information exposure
- Baseline Copilot and AI risk
- Review SharePoint information architecture
- Establish classification and metadata foundations
- Identify priority governance gaps
Why it matters
Clean, classified data is the foundation every later stage, and every AI outcome, is built on.
Protect What Matters
Build visibility across your Microsoft 365 information estate and identify where sensitive information, excessive access and governance gaps create risk.
What you get
Sensitive data actively protected, not just visible, with oversharing reduced across the estate.
What we do
- Remediate oversharing and excessive access
- Tighten internal and external permissions
- Implement and tune DLP
- Apply sensitivity and information protection controls
- Extend appropriate protection to endpoints
- Introduce controls progressively to minimise user friction
Why it matters
Enforced protection is what makes it safe to expand access, including for Copilot and agents.
Govern, Prove and Scale.
What you get
A governed, compliant, AI ready environment, with the evidence to prove it on demand.
What we do
- Map Microsoft 365 controls to applicable compliance requirements
- Establish audit-ready reporting and evidence
- Monitor governance and configuration drift
- Review access and sharing over time
- Govern emerging AI capabilities and agents
- Roll out Copilot progressively by cohort or use case
Why it matters
This is where the return on the first two stages gets realised, safely and on your terms.
WHY INSENTRA
Microsoft expertise, proven at scale most partners never reach.
4M+ Office 365 seats enabled
Delivered 5500+ projects
Microsoft Advance Specialisations
Expertise across Modern Work, spanning identity, adoption, teamwork and endpoint modernisation.
95 NPS score
A track record of trusted delivery and client experiences that consistently earn strong recommendations.
FAQ’s
Information Management, Governance and Compliance brings together the practices and Microsoft technologies needed to organise, protect and govern information across your Microsoft 365 environment.
Insentra’s IMGC approach helps you understand what information you have, reduce unnecessary exposure, strengthen governance and compliance controls, and create a trusted information foundation for Copilot, AI agents and automation.
Copilot works with information users already have permission to access.
If your Microsoft 365 environment contains overshared files, outdated permissions, poorly classified information or unmanaged content, introducing Copilot can make those existing issues more visible and more consequential.
Good information governance helps you understand and reduce those risks before expanding AI adoption.
No.
The goal is not to make everything perfect before you start.
Our staged approach helps you identify the highest priority information and access risks first, put appropriate controls in place and progressively expand your governance and AI capabilities.
This allows you to demonstrate value while managing risk at each stage.
The scope depends on your environment, risks and priorities.
An engagement can include information discovery and classification, SharePoint information architecture and metadata, sensitivity labels, retention, data loss prevention, permissions and oversharing remediation, AI readiness assessment, data security posture management and ongoing governance.
Rather than applying the same programme to every organisation, we identify where you are today and build an appropriate path forward.
It does not have to.
Our staged approach is designed to begin with discovery, classification and visibility before moving into broader enforcement.
For example, data loss prevention controls can initially be introduced in simulation so risks can be identified and policies refined before they affect users.
The objective is to improve protection without creating unnecessary friction for the people doing their jobs.
IMGC can help align Microsoft 365 information controls and governance practices with relevant regulatory and policy requirements, including the Privacy Act, Australian Privacy Principles, PSPF and GDPR where applicable.
This can include retention, information protection, access controls, monitoring and evidence to support your compliance posture.
The specific requirements and controls will depend on your organisation, regulatory obligations and environment.
Having the technology is only part of the solution.
Effective information governance also requires decisions about classification, information architecture, permissions, retention, policies, operating processes and how controls should be implemented without unnecessarily disrupting users.
IMGC helps turn Microsoft capabilities into a practical governance model that works across your organisation.
It can be both.
Initial work typically establishes the foundation and implements the controls needed to improve your information environment.
Ongoing governance can then help monitor and tune those controls, identify configuration or classification drift, review access and sharing, and govern new Copilot capabilities and AI agents as your environment evolves.
Find out exactly what is exposed in your Microsoft 365 environment.
Understand where sensitive information, excessive permissions and governance gaps could create risk as you scale Copilot and AI.
A practical path from visibility to AI readiness.
- See the risk
Identify sensitive information, oversharing and excessive permissions. - Reduce the risk
Prioritise remediation and strengthen protection. - Scale with confidence
Build a governed foundation for Copilot and AI.
Start with a clear view of your risk and where to focus first.